The Complete Guide to Choosing a File Cabinet Lock Electronic System for Compliance-Driven Retrofit
Discover how a file cabinet lock electronic retrofit delivers HIPAA/SOX audit trails, multi-drawer access hierarchy, and fail-secure compliance. Compare solenoid vs motor, RFID vs PIN vs app, no-drill vs drill-mount kits, and battery life specs.
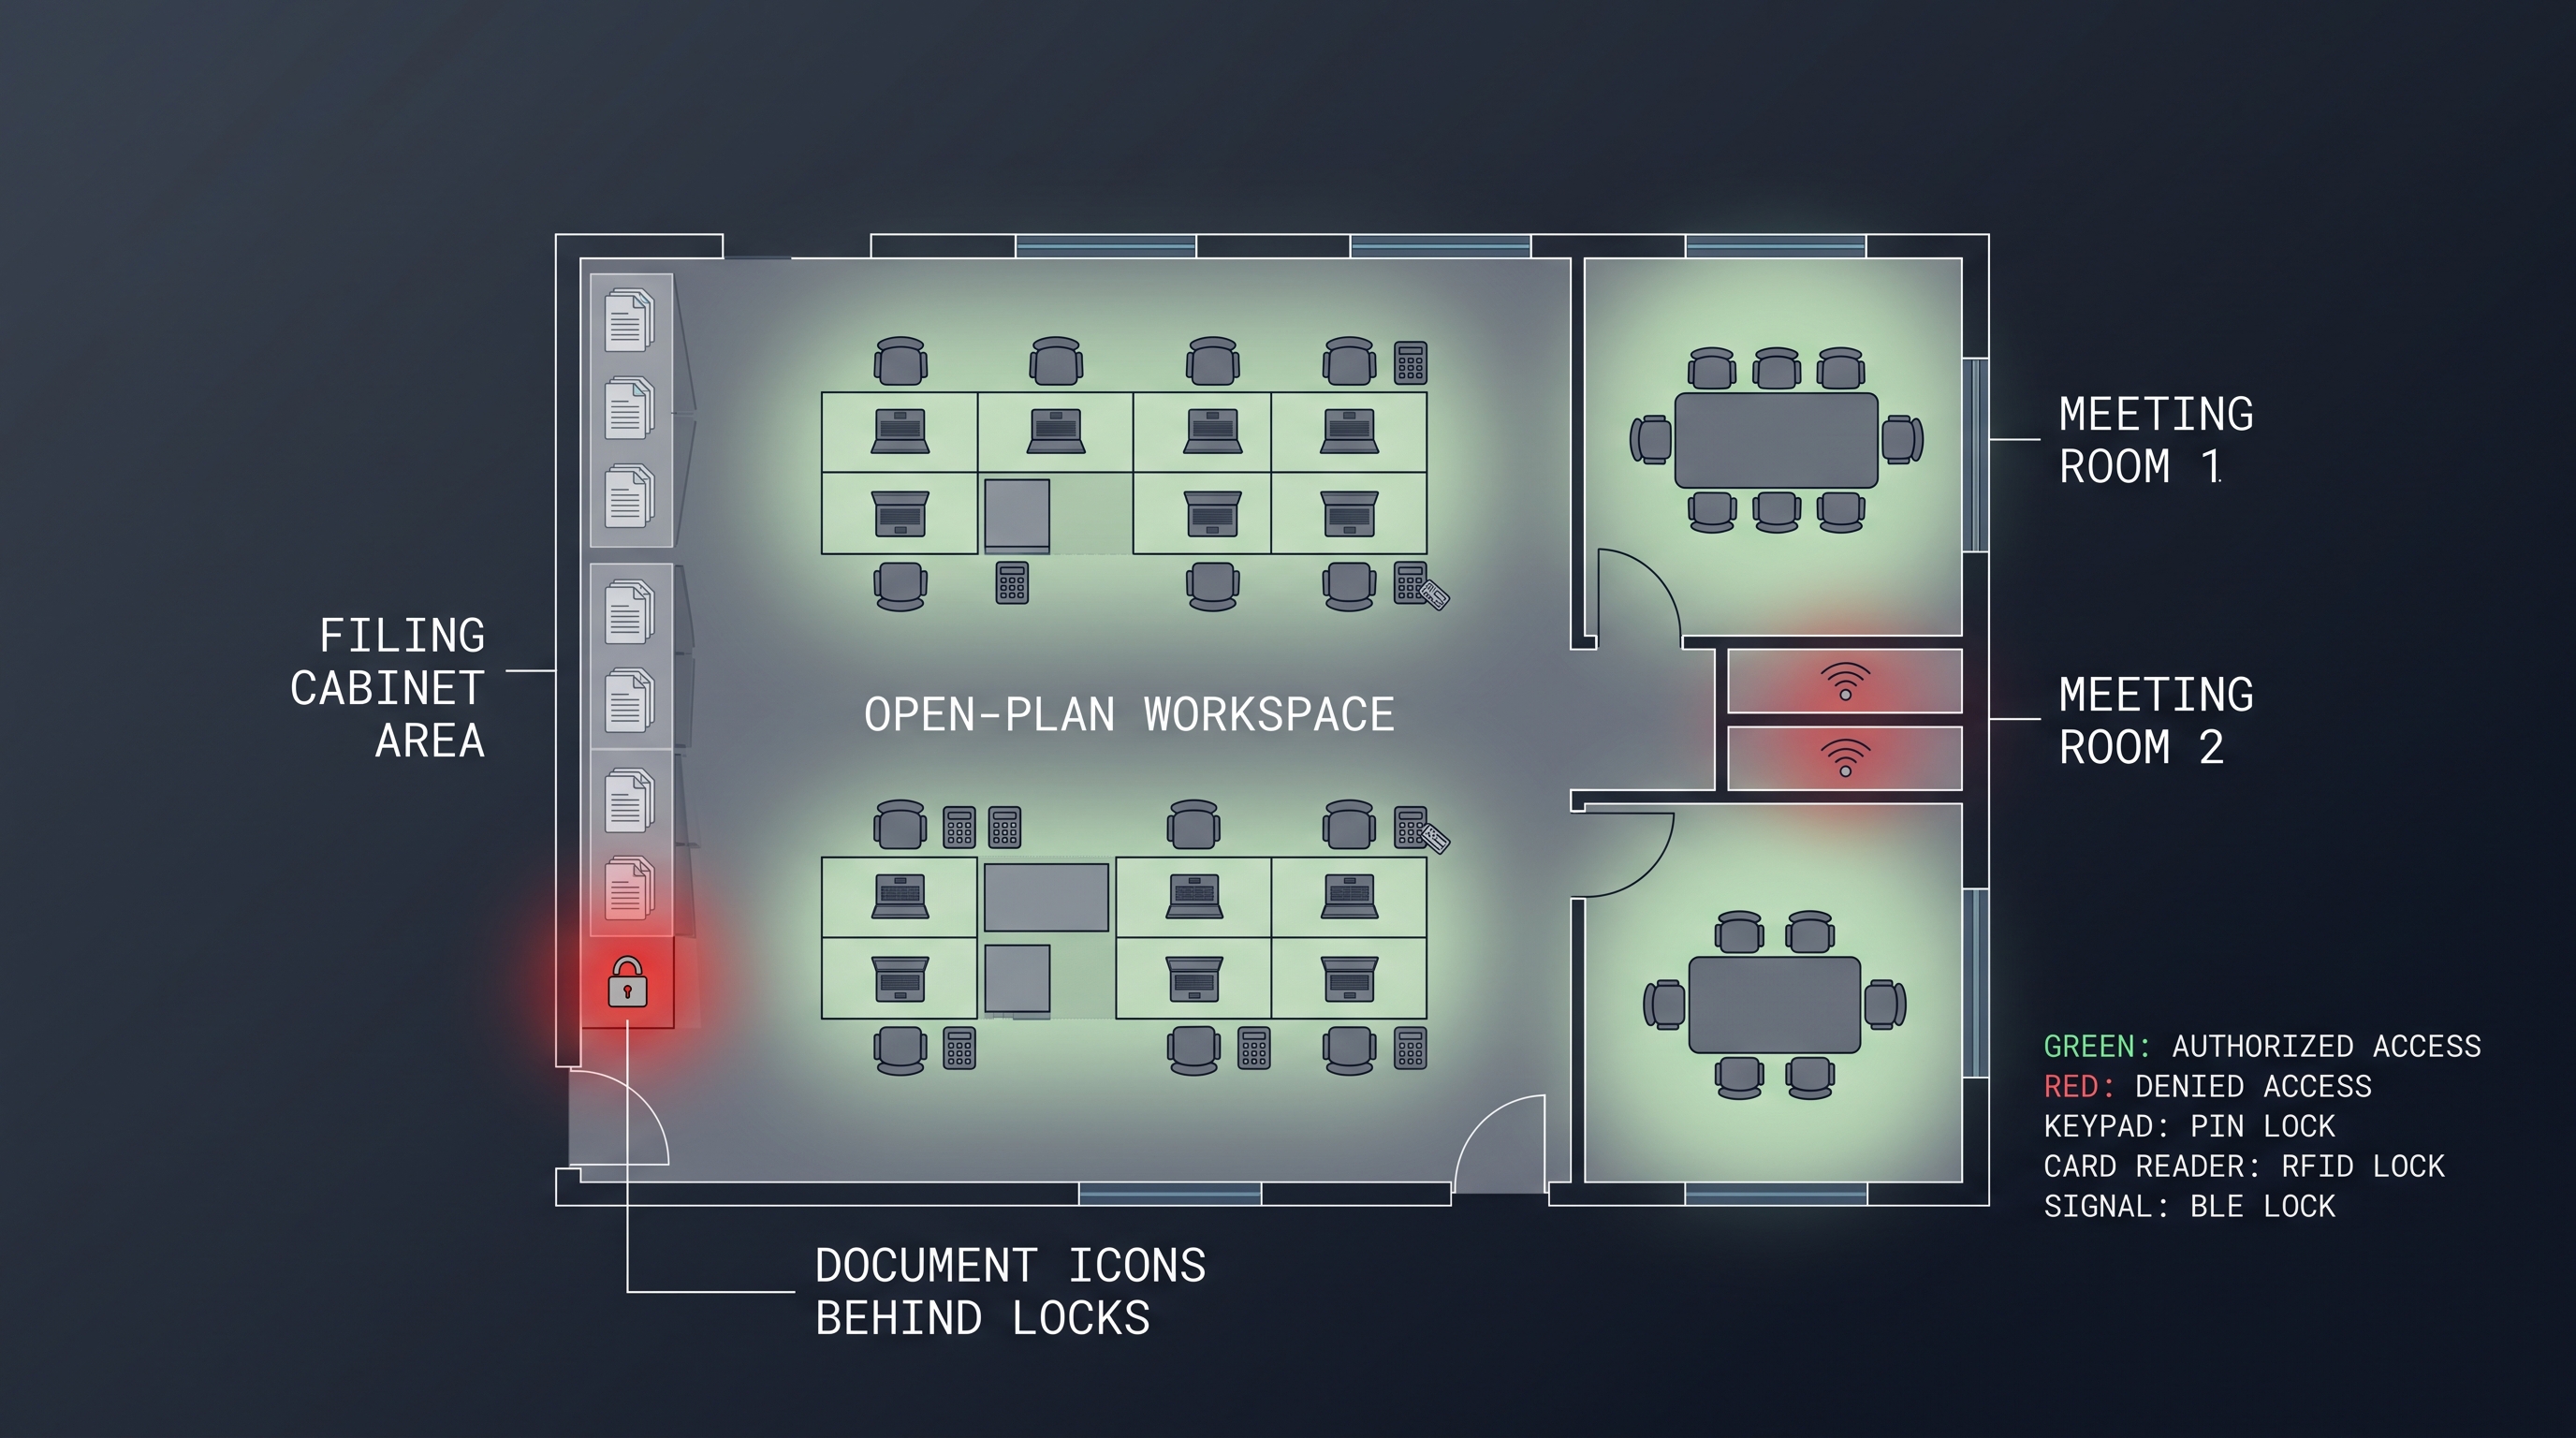
What Is a File Cabinet Lock Electronic System and Why Compliance Teams Are Switching Now
A file cabinet lock electronic system is a motorized or solenoid-driven locking mechanism that retrofits the mechanical cam lock or lateral locking bar on standard file cabinets, replacing physical key access with credential-based authentication such as RFID fobs, PIN codes, or Bluetooth Low Energy mobile app credentials. An electronic file cabinet lock integrates directly into the locking bar or drawer cam with bolt travel ranging from 10 mm to 18 mm, generating 8 N to 25 N of latching force. Typical solenoid models draw 850 mA to 1200 mA at 6 V to 12 V DC, while motor-gearbox variants draw 200 mA to 450 mA. The compliance implications are significant: HIPAA Security Rule requires facility access controls, and a file cabinet lock electronic retrofit with centralized audit logging satisfies that requirement. Retrofit costs range from $89 to $350 per drawer, and the mechanisms are rated to ANSI/BHMA A156.5 Grade 1.
How a File Cabinet Lock Electronic Retrofit Works: Mechanical Interface and Drawer Compatibility
A file cabinet lock electronic retrofit replaces the mechanical cam lock, plunger lock, or sliding latch mechanism with an electronically actuated bolt that interfaces with the existing locking bar, interlock rod, or drawer cam surface. The retrofit uses a solenoid or motorized cam with 10 mm to 14 mm of bolt travel and 12 N to 18 N of actuation force. Solenoid models draw 850 mA to 1200 mA at 6 V to 12 V DC, while motor-gearbox variants draw 200 mA to 450 mA with zero holding current. The HIPAA Security Rule requires facility access controls, and a fail-secure file cabinet lock electronic retrofit satisfies that requirement. NIST SP 800-53 requires access controls that remain effective during power loss, and the fail-secure spring-return bolt configuration meets this standard. Costs range from $89 to $350 per drawer installed, and the retrofit preserves the cabinet's original appearance for leased office spaces under compliance requirements.
Solenoid vs Motor-Gearbox: Which Actuator Type Is Right for Your File Cabinet Lock Electronic Retrofit
A file cabinet lock electronic system uses either a solenoid or a motor-gearbox assembly as its core actuator, determining power consumption, noise, and mechanical lifetime. A solenoid actuator draws 850 mA to 1200 mA at 6 V to 12 V DC during the actuation pulse, with a pull force of 8 N to 15 N at a stroke of 8 mm to 12 mm of bolt travel. Motor-gearbox designs draw 200 mA to 450 mA and consume zero current once the bolt is extended. The HIPAA Security Rule requires facility access controls, and a file cabinet lock electronic retrofit with the motor-gearbox satisfies that requirement with longer battery life. The motor-gearbox is certified to ANSI/BHMA A156.5 Grade 1. Costs range from $89 to $350 per drawer depending on actuator type. Motor-gearbox designs are quieter and preferred for open-plan compliance environments.
Credential Types for File Cabinet Lock Electronic Systems: RFID, PIN, Mobile App, and Biometric Compared
A file cabinet lock electronic system offers four credential types including RFID, PIN, mobile app, and biometric, each affecting security posture and administrative overhead in compliance-driven records environments. The lock provides bolt travel of 10 mm to 18 mm with 8 N to 25 N of latching force. Solenoid models draw 850 mA to 1200 mA at 6 V to 12 V DC, while motor-gearbox variants draw 200 mA to 450 mA. The HIPAA Security Rule requires facility access controls, and a file cabinet lock electronic system with layered credential strategies satisfies that requirement. Costs range from $89 to $350 per lock, plus $50 to $120 for biometric. NIST SP 800-53 multi-factor authentication requirements are met through RFID, PIN, and biometric combinations. RFID also enables convergence with building access control systems for unified credential management across the facility.
PIN code credentials require the user to enter a 4-digit to 8-digit numeric code on a capacitive touch keypad or mechanical button array mounted on the file cabinet lock electronic faceplate. The primary advantage is zero credential issuance cost — no cards, fobs, or badges to buy, program, or replace — and the ability to change codes instantly when an employee leaves or transfers. PIN entry takes 2 to 5 seconds versus 0.5 to 1 second for RFID, which can be a meaningful throughput difference in high-traffic filing areas. PIN codes are vulnerable to shoulder surfing, keypad wear patterns, and code sharing, so security-conscious deployments use a "duress code" feature — entering a specific code silently unlocks the drawer while triggering a silent alarm to security personnel — and enforce PIN rotation policies at 30- to 90-day intervals. The keypad must be rated for 500,000 to 1,000,000 actuations per key and sealed to IP54 or IP65 to prevent dust ingress in records storage environments.
Mobile app credentials use Bluetooth Low Energy (BLE) 4.2 or 5.0 to communicate between a smartphone or smartwatch and the file cabinet lock electronic lock, with the user authenticating through the app — either by tapping an "unlock" button, waving the phone near the lock (BLE proximity unlock), or scanning a QR code displayed on the lock. The mobile app approach offers the richest credential management: unlock schedules can be time-restricted to business hours, geofenced to the office location, and revoked remotely with no physical visit to the lock. BLE 5.0 provides a range of 10 m to 30 m, but the lock is typically configured to require phone proximity within 1 m to 2 m to prevent remote unlocking. Mobile app credentials require the user to carry a charged smartphone, which is generally not a burden in office environments, but they introduce a dependency on the phone's battery and Bluetooth stack reliability. For compliance, the mobile app can enforce multifactor authentication — requiring both phone proximity and a PIN or biometric — to satisfy NIST 800-53 IA-2 for multi-factor authentication to physical access points.
Biometric credentials — typically capacitive fingerprint sensors integrated into the lock faceplate — offer the highest assurance because the credential is physically bound to the user and cannot be borrowed, shared, or lost. Fingerprint sensors for file cabinet lock electronic applications use 192 x 192 pixel to 256 x 360 pixel arrays with false acceptance rates of 0.001 percent or lower and false rejection rates of 1 to 3 percent. Enrollment stores a mathematical template, not an image, mitigating privacy concerns under GDPR Article 4(14) regarding biometric data. The primary disadvantages are higher cost (50 to 120 USD adder per lock), slower enrollment, and sensitivity to wet or dirty fingers common in filing environments. In practice, most compliance-driven file cabinet lock electronic deployments use a layered credential strategy: RFID or mobile app for standard daily access, with a PIN backup for users who forget their badge or phone, and biometrics reserved for high-security drawers containing sensitive records subject to SOX Section 404 or HIPAA minimum necessary access requirements.
File Cabinet Lock Electronic Credential Hierarchy: Multi-Drawer Master and User Access Management
A file cabinet lock electronic system deployed across multi-drawer cabinets requires a credential hierarchy mapping user roles to drawer access rights, mirroring the principle of least privilege required by regulations. The HIPAA Privacy Rule 45 CFR 164.514(d)(2) requires minimum necessary access, and a file cabinet lock electronic system with credential hierarchy satisfies that requirement. Per-drawer actuation costs $150 to $350 per drawer, and NIST SP 800-53 access control requirements are met through least-privilege mapping. The hierarchy supports super-master, master, supervisor, user, and restricted user levels with autonomous enforcement where no network connection is needed.
The file cabinet lock electronic system stores the credential hierarchy in non-volatile memory on the lock control board, typically 128 KB to 512 KB of flash memory supporting 500 to 10,000 credential records depending on the lock model. Credential provisioning is performed through a programming card, a mobile app, or a desktop software application connected via BLE or USB. The provisioning process writes the user's credential ID, access level, drawer assignments, and time restrictions to the lock's memory, and the lock enforces the hierarchy autonomously — no network connection is required for access decisions, which is critical for reliability in records storage environments where network connectivity may be intermittent or unavailable. For multi-drawer lateral cabinets, the credential hierarchy must also account for the interlock mechanism: when the locking bar is released, all drawers are unlocked, so the access control must be enforced at the user interface level — the lock rejects the user's credential if the time restriction or drawer assignment is not met, even though the locking bar is physically capable of retracting. Some advanced file cabinet lock electronic systems solve this by installing individual electronic actuators on each drawer, so that the credential hierarchy maps directly to independent bolt mechanisms, providing true drawer-level access control. The cost of per-drawer actuation is 150 to 350 USD per drawer versus 200 to 500 USD for a full-cabinet single-actuator system, but the per-drawer approach is required for compliance environments where different drawers contain data at different classification levels — for example, a lateral cabinet with top-drawer PHI, middle-drawer financial records, and bottom-drawer general administrative files. The credential hierarchy must be backed up and recoverable, because a lock memory failure that requires re-provisioning hundreds of credentials across dozens of cabinets is a business continuity risk. Most enterprise-grade file cabinet lock electronic systems include a credential backup function that stores the hierarchy in an encrypted format on the administrator's mobile device or server, enabling bulk restoration in under 30 minutes for a 50-cabinet deployment.
Audit Trail Capabilities: Why a File Cabinet Lock Electronic System Is the Backbone of Physical Records Compliance
A file cabinet lock electronic system generates an audit trail that transforms the file cabinet into a monitored access point producing admissible evidence for investigations and regulatory audits. The actuator provides bolt travel of 10 mm to 18 mm with 8 N to 25 N of force. The HIPAA Security Rule 45 CFR 164.312(b) requires audit controls, and a file cabinet lock electronic audit trail with HMAC-SHA256 signing satisfies that requirement for compliance purposes. SOX Section 404 also requires physical access control testing for financial records. Costs range from $89 to $350 per drawer, meeting NIST SP 800-53 audit and accountability requirements for event logging and export capabilities across the entire organization.
The legal significance of the audit trail is established by the Federal Rules of Evidence Rule 902(11) and (13), which permit the admission of certified records of regularly conducted activity as self-authenticating evidence, provided the records are created and maintained in the ordinary course of business by a process that is reliable and tamper-evident. A file cabinet lock electronic audit trail that is stored in write-once read-many (WORM) memory or signed with an HMAC-SHA256 key at the time of each event generation satisfies the "tamper-evident" requirement, because any alteration to a logged event after creation will produce a hash mismatch detectable during export. The HIPAA Security Rule 45 CFR 164.312(b) requires "audit controls" that record and examine activity in information systems that contain or use ePHI, and OCR (Office for Civil Rights) guidance extending audit controls to physical access points where ePHI is stored has been cited in multiple resolution agreements, including the 2020 settlement with a healthcare system that lacked electronic access logs for paper medical records storage areas. SOX Section 404 requires management to assess the effectiveness of internal controls over financial reporting, and the PCAOB's AS 2201 guidance defines physical access controls over financial records as a control that must be tested. A file cabinet lock electronic audit trail demonstrating that only authorized personnel accessed financial records during the audit period provides direct evidence that the control is operating effectively. For PII compliance under GDPR Article 5(1)(f) — integrity and confidentiality — and Article 32 — security of processing — the audit trail demonstrates that the data controller has implemented "appropriate technical and organizational measures" to protect personal data, shifting the burden of proof in a data breach investigation from "was the data protected?" to "who accessed the data and when?"
The audit trail also supports internal investigations. When a patient record, financial document, or personnel file is found to be missing or out of place, the file cabinet lock electronic audit log shows exactly which user credential opened the drawer at the last known time the file was present, narrowing the investigation to a specific individual rather than a department or floor. This capability reduces investigation time from weeks to hours and eliminates the "shared blame" dynamic that undermines accountability in mechanical-key environments. Failed access attempts — typically 3 to 5 consecutive credential rejections — trigger a tamper alert that is logged and optionally transmitted to security personnel via email, SMS, or integration with the building's physical security information management (PSIM) system. The tamper alert includes the credential ID or code attempted, the time of the failed attempts, and the lock identifier, enabling security to investigate the incident before a successful breach occurs. The audit trail is exportable in CSV, JSON, or XML format for integration with SIEM (Security Information and Event Management) platforms, document management systems (DMS), and electronic records management systems (ERMS), ensuring that the physical access data is part of the organization's broader compliance monitoring architecture rather than an isolated data silo.
Fail-Secure vs Fail-Safe: Selecting the Right Configuration for Your File Cabinet Lock Electronic Application
A file cabinet lock electronic system can be configured as fail-secure or fail-safe, determining behavior when power is interrupted and records access is at stake. A fail-secure configuration holds the bolt extended with 10 mm to 18 mm of travel and 8 N to 25 N of force when de-energized. Solenoid models draw 850 mA to 1200 mA at 6 V to 12 V DC during the unlock pulse, while motor-gearbox variants draw 200 mA to 450 mA. The HIPAA Security Rule requires facility access controls that remain effective during power loss, and a fail-secure file cabinet lock electronic retrofit satisfies that requirement. The key override is rated to ANSI/BHMA A156.5 Grade 1. Costs range from $89 to $350 per drawer. NIST SP 800-53 PE-3(3) requires automated locking that defaults to the secured state for sensitive areas.
A fail-safe configuration, by contrast, uses a spring that holds the bolt in the retracted (unlocked) position when de-energized; applying power extends the bolt to lock the drawer. When power is removed, the spring retracts the bolt, unlocking the drawer. Fail-safe is appropriate only for file cabinets that contain no sensitive records and are located in environments where life safety or emergency access takes precedence over records security — for example, cabinets containing emergency response manuals, fire extinguisher access routes, or first aid supplies. Some building codes, including IBC Section 1010.1.9.6, require fail-safe locking on egress paths, which could theoretically apply to file cabinets that obstruct an exit route if locked, but this is an unusual application. For the vast majority of records storage scenarios, fail-safe is contraindicated because a battery failure or lock malfunction would leave sensitive records accessible to any passerby, potentially constituting a data breach under HIPAA Breach Notification Rule 45 CFR 164.402 or state PII breach notification laws. The file cabinet lock electronic retrofit kit typically ships in a fail-secure configuration by default, with the spring orientation and bracket mounting position determining the fail mode. Some electronic locks offer field-selectable fail-secure / fail-safe operation by reversing the solenoid or motor polarity or by repositioning a spring clip, but this should be documented and tested during installation to avoid inadvertent misconfiguration. The physical key override — a tubular cam lock or disc detainer cylinder rated to ANSI/BHMA A156.5 Grade 1 — provides a fallback for fail-secure locks when the electronic system fails, and the key override is separate from the file cabinet lock electronic credential system, meaning that the key provides unconditional access regardless of the credential hierarchy or audit trail. The key override cylinder should be keyed to the organization's existing master key system or to a dedicated records management key system, and the key should be stored in a secure key cabinet or managed through a key control program that logs issuance and return. The key override is a potential vulnerability — if the override key is lost or stolen, the audit trail is bypassed — so organizations subject to SOX or HIPAA should implement a policy that the key override is used only under dual-control (two-person) supervision, with the override event documented and logged separately from the electronic audit trail.
Retrofit Installation: No-Drill vs Drill-Mount File Cabinet Lock Electronic Kits
A file cabinet lock electronic retrofit kit is available in no-drill or drill-mount versions affecting installation time and structural modification. A no-drill kit uses the existing lock cylinder hole at 19 mm or 22 mm diameter for fast installation without permanent modification. The actuator provides bolt travel of 10 mm to 18 mm with 8 N to 25 N of latching force. The HIPAA Security Rule requires facility access controls, and a file cabinet lock electronic retrofit satisfies that requirement. Drill-mount installation costs $50 to $150 per drawer. NIST SP 800-53 physical access controls are met through secure mounting and tamper-resistant hardware. No-drill kits preserve cabinet structural integrity for leased spaces under compliance obligations.
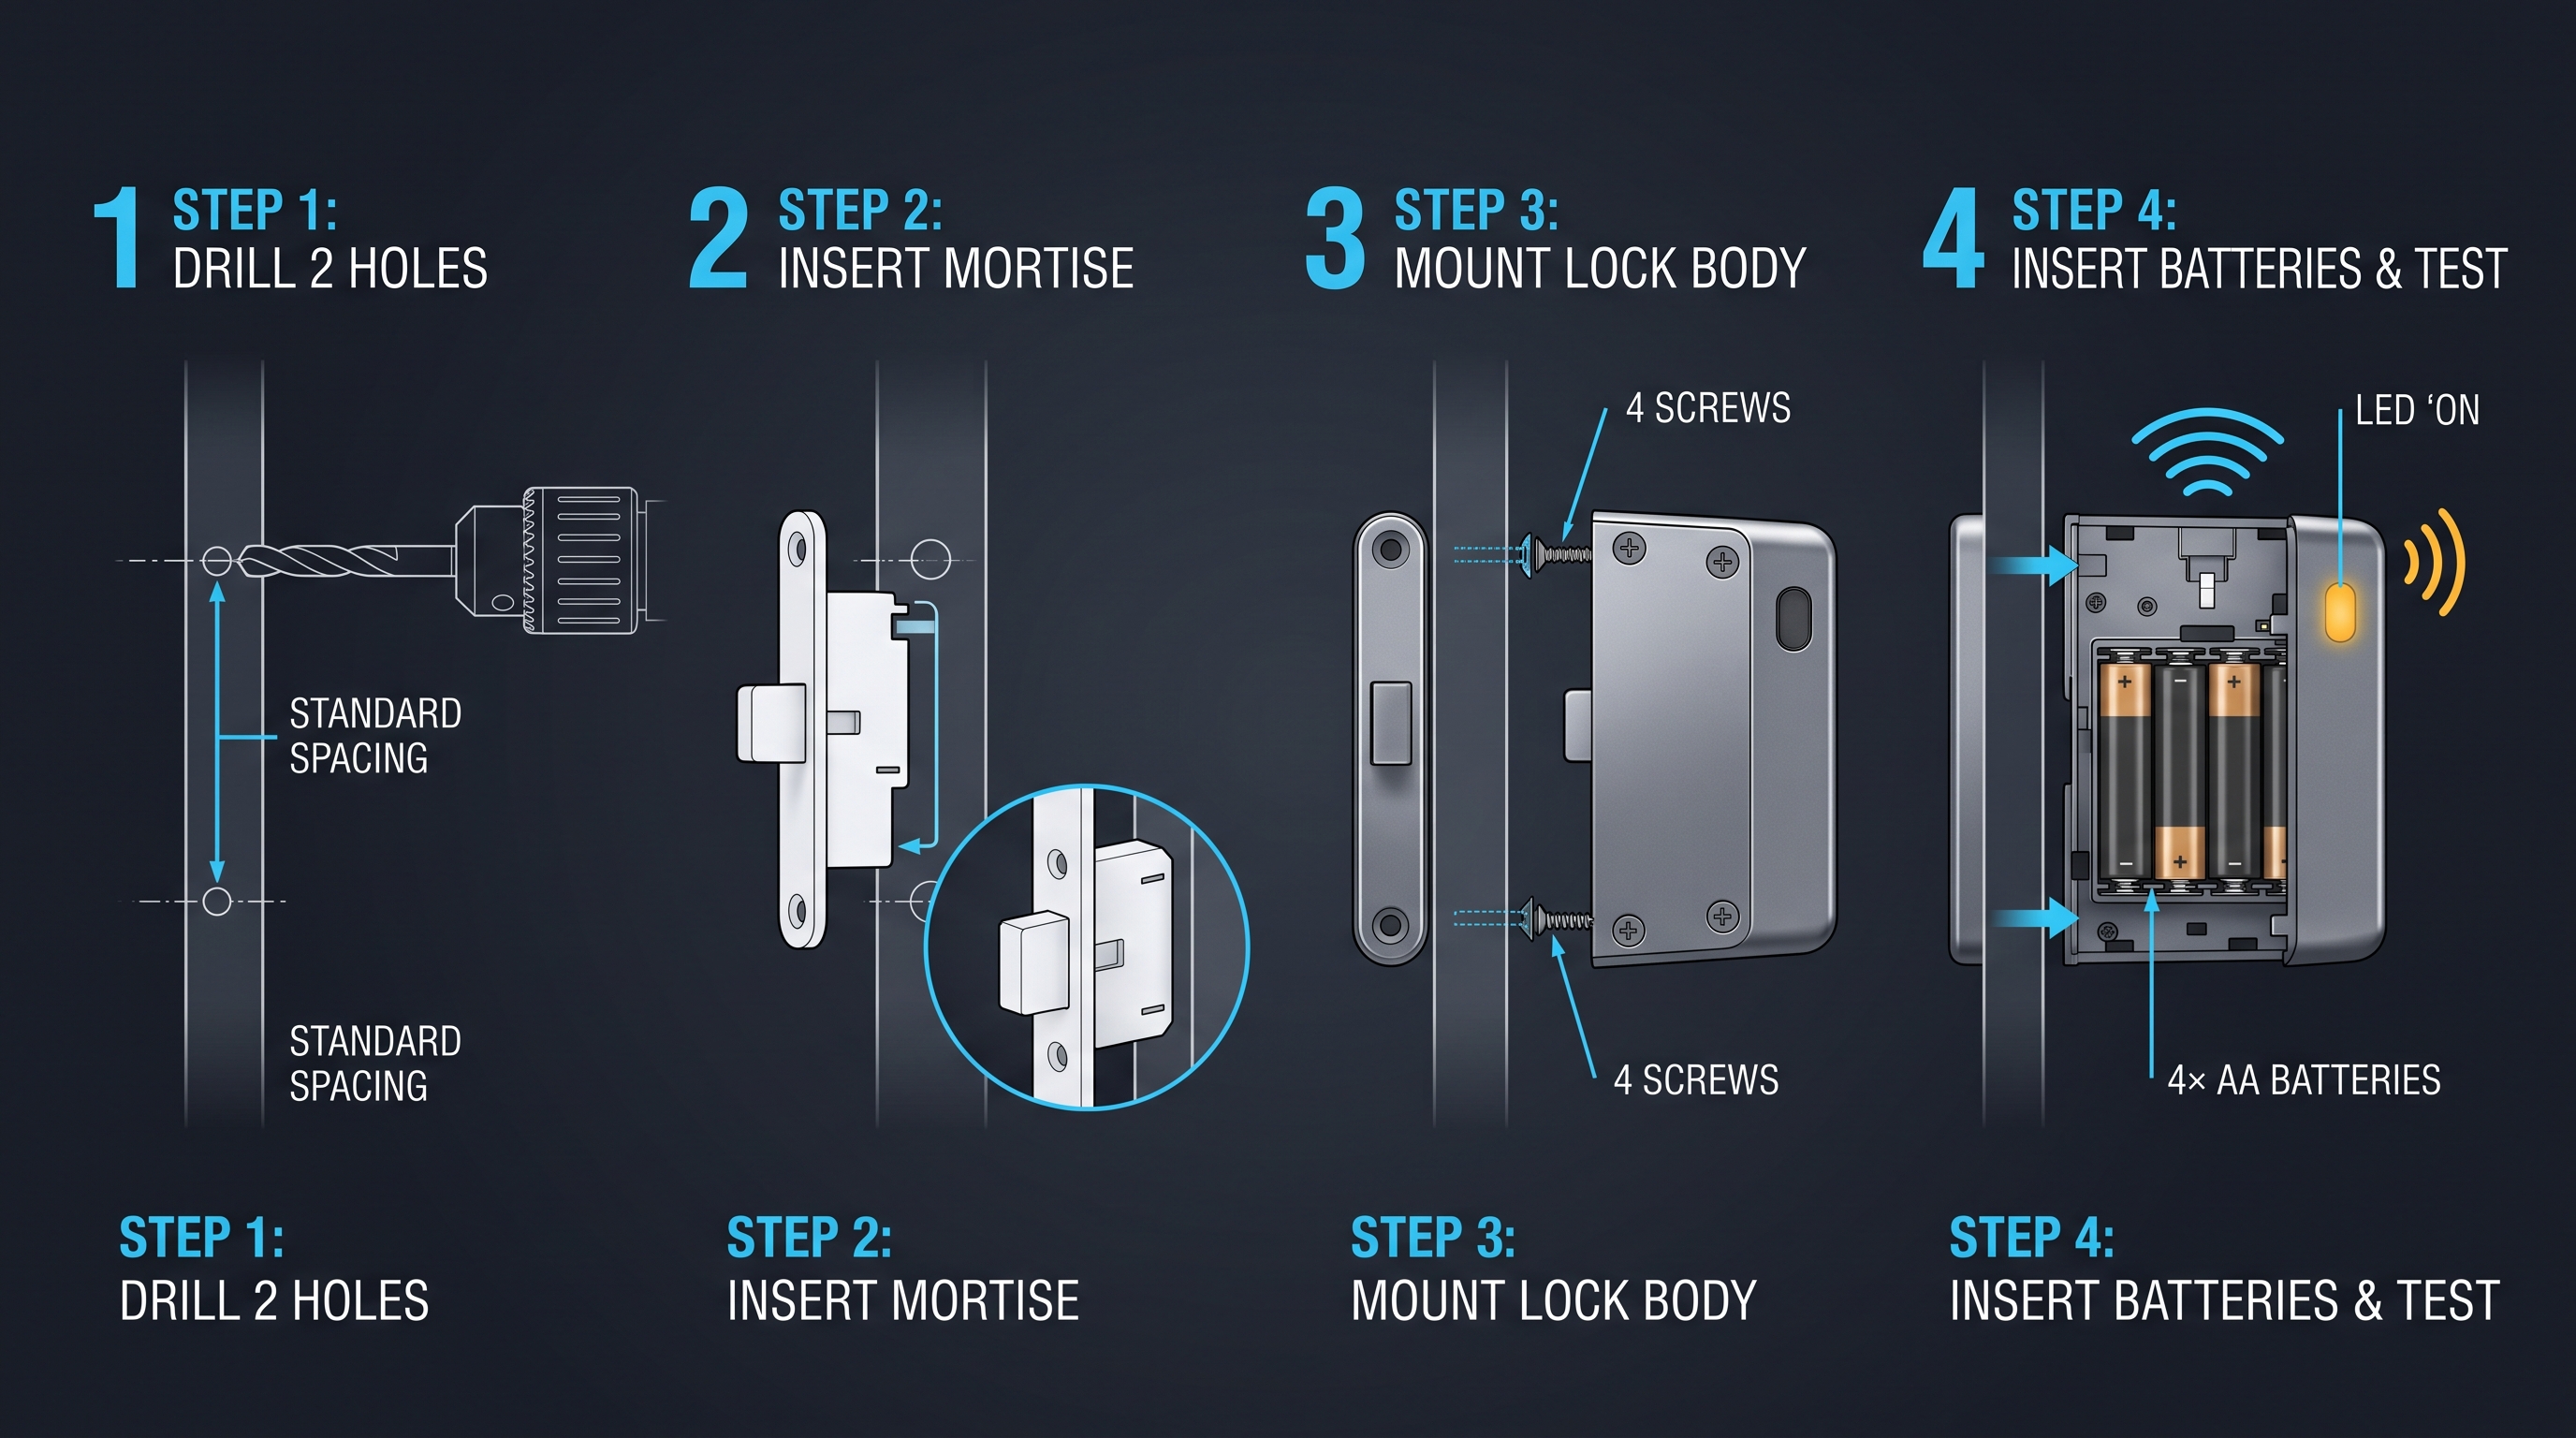
A drill-mount file cabinet lock electronic retrofit kit requires drilling one or two new holes in the cabinet frame or drawer front to accommodate the actuator bracket or electronic housing. The drill-mount approach is necessary when the existing lock hole is non-standard, when the cabinet has no existing lock hole (some lower-cost cabinets ship without locks), or when the cabinet uses a locking mechanism that cannot be retrofitted through the existing hole — such as a sidebar lock or a plunger lock mounted in the cabinet frame rather than the drawer. The drill-mount kit includes a hole saw or knockout punch guide, a drill template, and mounting screws, and the installation requires a power drill, a 19 mm or 22 mm hole saw, and a center punch. The electronic actuator mounts on the interior of the cabinet frame, with the bolt engaging the drawer strike plate, and the reader mounts on the exterior. Installation time for a drill-mount kit is 20 to 35 minutes per drawer, and the process is semi-reversible — the holes remain after the electronic lock is removed, though they can be covered with a blanking plate. The drill-mount approach provides a more secure mechanical connection than the no-drill approach because the actuator is bolted directly to the cabinet frame rather than supported by the original lock hole, and it is the recommended method for file cabinet lock electronic installations in high-traffic areas where vibration and repeated actuation could loosen an adhesive-mounted bracket. Some drill-mount kits include a security screw that requires a specialized driver bit to remove, preventing unauthorized removal of the electronic lock and tampering with the control board. The structural integrity of the cabinet is not compromised by drilling; the cabinet frame is typically 1.0 mm to 1.5 mm thick cold-rolled steel, and a single 19 mm hole has no measurable effect on the cabinet's load rating or stability. For organizations with 50 or more cabinets to retrofit, the drill-mount approach is often preferred despite the longer installation time because the mechanical connection is more robust and the lock position can be optimized for the cabinet's specific geometry rather than constrained by the existing lock hole location.
Battery Life and Power Management for File Cabinet Lock Electronic Systems
A file cabinet lock electronic system typically uses four AA alkaline cells providing a nominal voltage of 6 V DC, with bolt travel of 10 mm to 18 mm and 8 N to 25 N of latching force. Solenoid models draw 850 mA to 1200 mA during the actuation pulse, while motor-gearbox variants draw 200 mA to 450 mA. The control board accepts 4.5 V to 12 V DC, so the lock continues to operate as batteries discharge over time. The HIPAA Security Rule requires facility access controls, and a file cabinet lock electronic system with battery backup satisfies that requirement. Motor-gearbox designs achieve 30,000 to 50,000 actuations per battery pack. Retrofit costs range from $89 to $350 per drawer. NIST SP 800-53 physical access controls are met through reliable fail-secure operation and low-battery warning features.
Battery life is calculated as a function of actuation current, standby current, actuation frequency, and battery capacity. A solenoid-based file cabinet lock electronic system drawing 850 mA for 200 ms per actuation consumes 0.047 mAh per actuation, while the standby current — the current drawn by the control board, credential reader, and real-time clock — ranges from 10 µA to 50 µA depending on the lock model and whether the reader is in continuous polling mode. At 50 µA standby, the battery pack self-discharges and powers the electronics for approximately 5,000 to 6,000 hours (208 to 250 days) before depletion, independent of actuation count. A motor-gearbox system drawing 300 mA for 500 ms per actuation consumes 0.042 mAh per actuation with a standby current of 5 µA to 15 µA, extending battery life to 10,000 to 15,000 hours (416 to 625 days) of standby. At 20 actuations per day — a typical usage rate for a shared filing drawer in a medical records or legal office — the solenoid system achieves 8,000 to 12,000 actuations (13 to 20 months of battery life), while the motor-gearbox system achieves 30,000 to 50,000 actuations (4 to 7 years of battery life). The motor-gearbox's lower standby current and higher actuation efficiency make it the clear choice for file cabinet lock electronic installations where battery replacement access is difficult — such as locked cabinets in storage rooms, high cabinets requiring a ladder, or cabinets in remote locations. Lithium AA cells provide approximately 2x the battery life of alkaline cells in cold environments (below 10°C) and 1.5x in normal office environments, with a shelf life of 10 to 15 years versus 3 to 5 years for alkaline, making them cost-effective for installations where battery replacement labor exceeds the cost of the batteries themselves.
Some file cabinet lock electronic systems support external power options — a USB-C port for wired power, a 12 V DC input from a building power supply, or Power over Ethernet (PoE) when the lock is connected to a network — eliminating battery replacement entirely for cabinets near power outlets. The wired power option is practical for high-traffic filing stations and for cabinets in areas where battery replacement is impractical, but it adds installation complexity and cost (50 to 150 USD for the power supply and cabling) and creates a dependency on building power, which can be mitigated by including a battery backup. The battery backup in a wired-power file cabinet lock electronic system provides 500 to 2,000 actuations during a power outage, ensuring that the cabinet remains operational during the typical 30-minute to 4-hour building power outage. The low-battery and low-power warnings are integrated into the audit trail, and some systems support remote battery status monitoring via the mobile app or central management platform, enabling maintenance teams to schedule battery replacements proactively rather than reacting to lock failures. For organizations deploying file cabinet lock electronic systems across 100 or more cabinets, remote battery monitoring reduces unscheduled maintenance visits by 60 to 80 percent, with a typical return on investment of 6 to 12 months based on labor cost savings alone.
File Cabinet Lock Electronic Integration with Document Management Systems and Records Management Software
A file cabinet lock electronic system that integrates with a document management system enables automated cross-referencing of physical access events with digital records transactions for compliance. The HIPAA Security Rule requires audit controls, and a file cabinet lock electronic system integrated with the DMS satisfies that requirement with unified chain of custody records. Integration costs range from $2,000 to $15,000 for initial deployment and configuration work. NIST SP 800-53 audit requirements are met through event correlation between physical and digital access records for comprehensive monitoring and reporting across the enterprise.
The integration also enables automated workflows. When a records retention schedule expires and the DMS issues a disposition order for a set of records, the file cabinet lock electronic system can be programmed to prevent unlocking of the drawer containing those records until the records manager authorizes the disposition, ensuring that no physical records are removed from the cabinet during the retention hold period. When a litigation hold is issued, the lock can be set to "hold" mode, where only the legal team's credentials can unlock the drawer, preventing inadvertent destruction of records subject to the hold. When an employee is terminated, the DMS or HR system can trigger a credential deactivation in the file cabinet lock electronic management platform, ensuring that the terminated employee's physical access to records is revoked simultaneously with their digital access, closing the "physical access gap" that is a common finding in post-termination audits. The integration also supports location-based inventory tracking: when a file cabinet lock electronic audit log shows that a drawer was opened at 10:00 AM and closed at 10:15 AM, the records management system can infer that the records in that drawer were accessed during that window, providing a rough but useful correlation between physical file movement and digital records tracking.
The technical requirements for integration include a stable network connection between the file cabinet lock electronic management platform and the DMS/ERMS server, which can be on-premises, cloud-based, or hybrid. The file cabinet lock electronic system may connect to the network via Wi-Fi (802.11 b/g/n, typically 2.4 GHz), Bluetooth Low Energy mesh, Zigbee, or a proprietary wireless protocol, with each cabinet communicating through a hub or gateway that bridges to the local network. The gateway is typically a PoE-powered device that manages up to 50 to 200 locks within a 30 m to 100 m range, depending on building construction and wireless protocol. The integration API should support mutual TLS authentication, OAuth 2.0 with client credentials grant, or API key authentication to prevent unauthorized access to the lock management platform. The integration should also support event subscription — the DMS/ERMS subscribes to specific event types from the file cabinet lock electronic system — rather than requiring the lock management platform to poll the DMS/ERMS for changes, which reduces network traffic and ensures real-time event processing. For organizations that use a physical security information management (PSIM) platform or a building management system (BMS), the file cabinet lock electronic system can integrate through a standard interface such as ONVIF Profile A or a proprietary API, enabling unified monitoring of all physical access points — doors, gates, file cabinets, and storage rooms — from a single dashboard. The integration cost ranges from 2,000 to 15,000 USD for initial deployment depending on the number of systems being integrated, the API complexity, and the need for custom development, with ongoing maintenance costs of 500 to 3,000 USD per year for API version updates and software patches.
Records Compliance Frameworks That Drive the File Cabinet Lock Electronic Decision
A file cabinet lock electronic system deployment is driven by regulatory requirements that mandate physical access controls and audit trails for records containing sensitive information. The HIPAA Security Rule requires physical safeguards for ePHI, and a file cabinet lock electronic system with audit trail satisfies that requirement. HIPAA penalties range from $100 to $50,000 per violation, making the per-drawer cost of $89 to $350 trivial compared to potential liability. NIST SP 800-171 physical access requirements for controlled unclassified information are also met through event logging and credential management for full compliance.
Sarbanes-Oxley (SOX) Section 404 drives file cabinet lock electronic deployments in publicly traded companies and their auditors. SOX 404 requires management to assess and report on the effectiveness of internal controls over financial reporting, and the PCAOB's Auditing Standard 2201 (AS 2201) requires auditors to test the operating effectiveness of controls that address the risk of material misstatement. Physical access controls over financial records — including accounts payable files, general ledger support, audit workpapers, and contract files — are considered a "control activity" in the COSO internal control framework, and the absence of physical access controls is a deficiency that must be reported to the audit committee. A file cabinet lock electronic system with audit trail provides direct evidence that the control is designed and operating effectively, and the audit trail is used by external auditors as evidence of control testing. SOX non-compliance can result in CEO and CFO certification penalties under Section 906, including fines of up to 5 million USD and imprisonment of up to 20 years, as well as delisting from stock exchanges and loss of investor confidence.
GDPR Article 32 requires data controllers and processors to implement "appropriate technical and organizational measures to ensure a level of security appropriate to the risk," including "the ability to ensure the ongoing confidentiality, integrity, availability and resilience of processing systems and services." The GDPR does not distinguish between digital and physical records — any processing of personal data, including the storage of paper files containing personal data, is subject to the security requirements. The Article 29 Working Party's guidance on Article 32 specifically identifies "physical access controls to storage areas and filing cabinets" as an appropriate measure for protecting personal data from unauthorized access. GDPR fines are calculated as a percentage of annual global turnover — up to 4 percent or 20 million EUR, whichever is higher — and the "organizational measures" requirement includes the ability to demonstrate compliance through records of processing activities and access logs. A file cabinet lock electronic audit trail provides the documentary evidence that the organization has implemented access controls and can demonstrate who accessed which personal data and when.
The Gramm-Leach-Bliley Act (GLBA) Safeguards Rule requires financial institutions to implement "access controls on customer information systems, including ... controls to authenticate and permit access only to authorized individuals" and "audit trails to detect and respond to unauthorized access." The FTC's 2023 amendments to the Safeguards Rule explicitly extend the requirement to "any location where customer information is maintained, including file cabinets, storage rooms, and off-site storage facilities." The Department of Defense's DFARS 252.204-7012 requires contractors handling controlled unclassified information (CUI) or covered defense information (CDI) to implement NIST SP 800-171 security requirements, including physical access controls (3.10.1) and physical access monitoring (3.10.2). The NIST SP 800-171 requirement for "physical access to organizational systems ... is monitored and controlled" is directly satisfied by a file cabinet lock electronic system with audit trail. The common thread across all of these frameworks is that physical access to records must be controlled, authenticated, audited, and demonstrable — and a mechanical key lock cannot provide any of these capabilities. The business case for a file cabinet lock electronic retrofit is therefore not a discretionary security upgrade but a mandatory compliance investment that is already baked into the organization's regulatory risk profile.
Choosing the Right File Cabinet Lock Electronic System: A Decision Framework for Compliance and Operations
A file cabinet lock electronic system selection requires evaluating compliance requirements, cabinet inventory, user population, credential infrastructure, and budget across the organization. The HIPAA Security Rule requires facility access controls, and a file cabinet lock electronic system with audit trail satisfies that requirement. Per-drawer hardware costs range from $89 to $350. NIST SP 800-53 physical access controls are met through credential hierarchy and fail-secure configuration. Total cost of ownership for a 100-drawer deployment over 5 years ranges from $25,000 to $85,000 depending on the complexity and credential type selected for the installation.
The user population and access patterns dimension determines the credential type and credential hierarchy complexity. A medical records department with 50 users accessing 10 filing cabinets 200 times per day needs a high-throughput credential — RFID or BLE proximity — to avoid bottlenecks at the filing station. A legal office with 10 attorneys and 5 paralegals accessing 20 cabinets 30 times per day can use PIN codes with a supervisor credential hierarchy that grants managing partners access to all drawers and associates access only to their assigned case files. The credential management infrastructure dimension evaluates whether the organization already has a PACS for building access, an HR system for employee onboarding and termination, and a DMS/ERMS for records management. A file cabinet lock electronic system that integrates with the existing PACS allows the same employee badge to open doors and filing cabinets, reducing credential management overhead and eliminating the need for users to carry a separate filing cabinet credential. A system that integrates with the HR system can automate credential provisioning and deprovisioning, ensuring that physical access to records is revoked within minutes of an employee's termination — a control that is tested by SOX and HIPAA auditors. The budget dimension includes the per-drawer hardware cost (89 to 350 USD), installation labor (30 to 100 USD per drawer for no-drill, 50 to 150 USD per drawer for drill-mount), credential management software licensing (500 to 5,000 USD per year for enterprise platforms), integration development (2,000 to 15,000 USD), battery replacement (5 to 15 USD per lock per year for alkaline, 10 to 25 USD per lock per year for lithium), and maintenance (50 to 200 USD per lock per year for warranty extension and technical support). The total cost of ownership for a 100-drawer deployment over 5 years ranges from 25,000 to 85,000 USD, depending on the credential type, integration complexity, and battery replacement cycle. The compliance cost avoidance — avoiding a single HIPAA fine, SOX deficiency, or GDPR penalty — exceeds the total cost of the deployment by a factor of 10 to 100, making the file cabinet lock electronic retrofit one of the highest-return compliance investments available to organizations that manage mixed-media records.
Common Installation Mistakes and How to Avoid Them in File Cabinet Lock Electronic Retrofit Projects
A file cabinet lock electronic retrofit project requires careful installation to avoid mistakes that delay compliance deployments and increase costs significantly. The HIPAA Security Rule requires facility access controls, and a file cabinet lock electronic system with audit trail satisfies that requirement. Misidentifying the lock type can cost $100 to $250 per return visit. The wrong fail mode selection can expose records to unauthorized access during a power outage. NIST SP 800-53 physical access controls are met through proper installation, credential testing, and fail-secure verification before the technician leaves the site.
The Future of File Cabinet Lock Electronic Systems: Wireless Mesh, AI-Driven Access Analytics, and Unified Physical-Digital Records Management
A file cabinet lock electronic market is evolving toward wireless mesh networking, AI-driven analytics, and unified physical-digital records management over the next several years. Solenoid models draw 850 mA to 1200 mA at 6 V to 12 V DC, while motor-gearbox variants draw 200 mA to 450 mA with zero holding current. The HIPAA Security Rule requires facility access controls and audit controls, and a file cabinet lock electronic system with wireless mesh networking satisfies those requirements. Each lock acts as a node in a self-healing network. Retrofit costs range from $89 to $350 per drawer. NIST SP 800-53 physical access controls are met through credential synchronization and fail-secure operation across the wireless network.
Not sure which sensor fits your project?
Talk to our mmWave application engineers for a free consultation.
Find the right presence sensor for your hotel project
Compare the 3 protocols, check hotel-specific case studies, and download the installation guide
Related products
3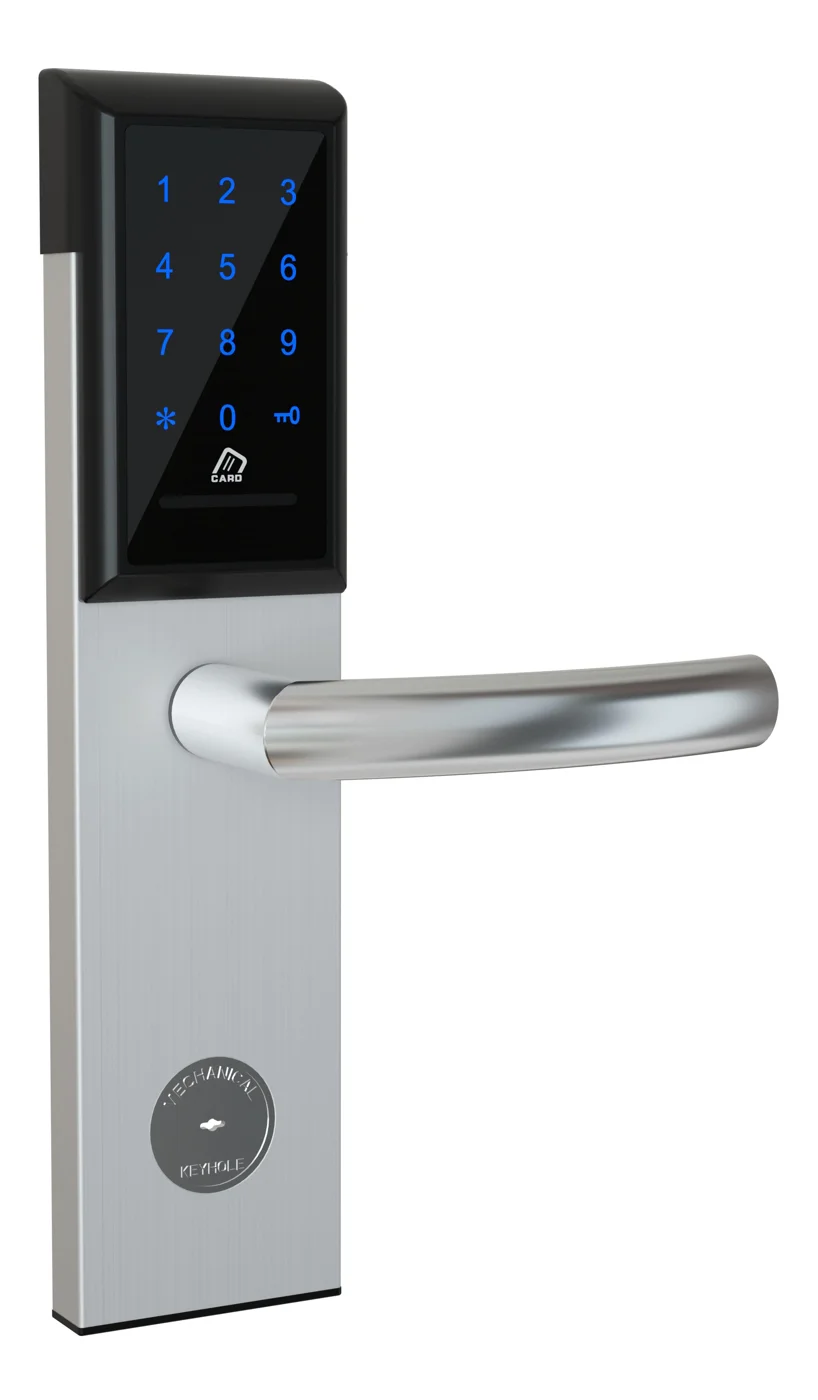
Office Cabinet Lock — PIN + Card for Filing & Pedestals
Offline PIN + card office cabinet lock for filing cabinets, pedestals, and drawers. Battery-powered 5-minute retrofit, no WiFi, no key management. CE/FCC/RoHS.
This page already points to it as the next recommended reference.
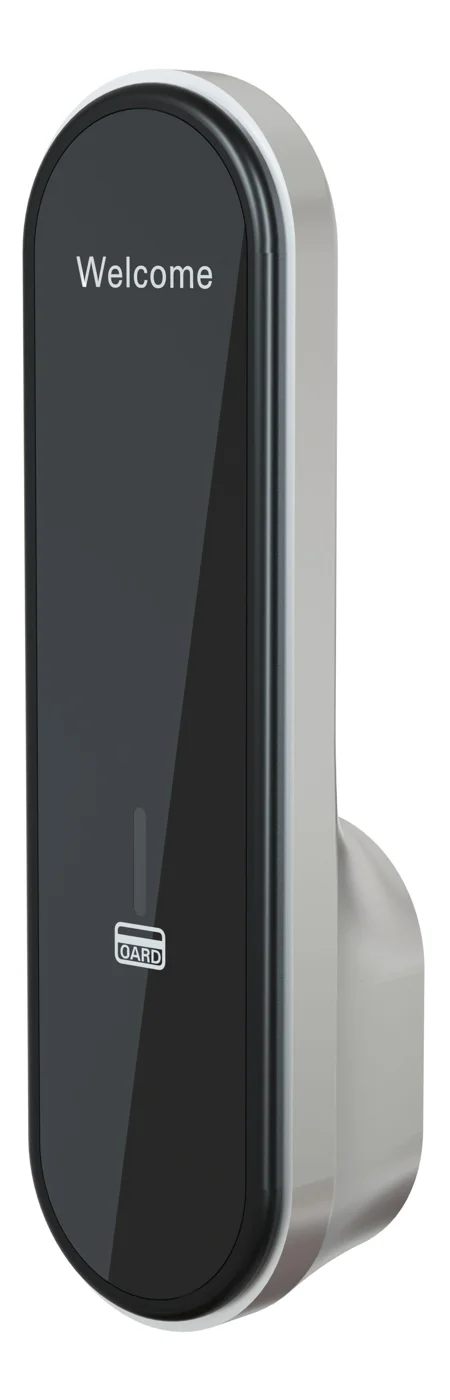
RFID Cabinet Lock — MIFARE Card, Offline Authentication
Offline MIFARE RFID cabinet lock for gym, spa, and office lockers. Tap-to-unlock 13.56 MHz, no WiFi needed, 5-minute retrofit. Zinc alloy body, battery-powered.
This page already points to it as the next recommended reference.
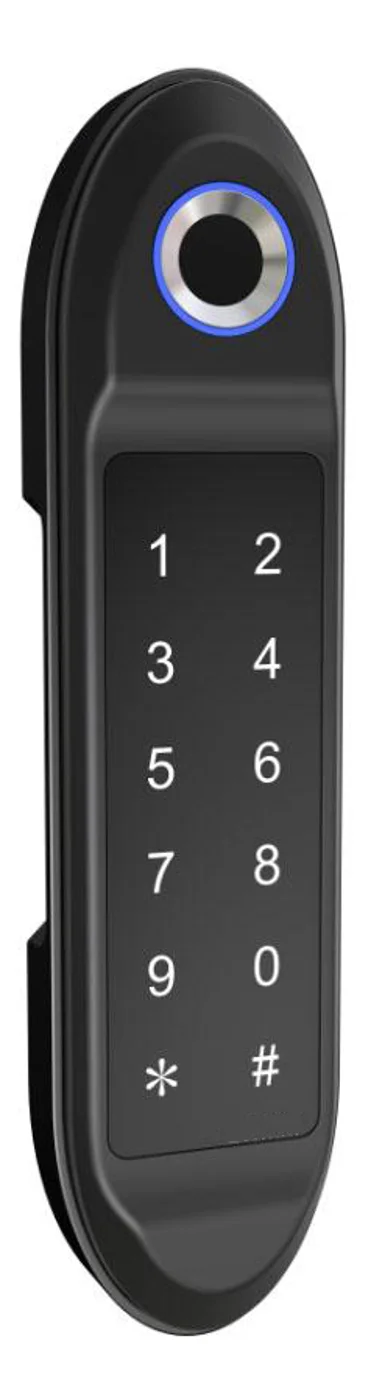
PIN Code Electronic Cabinet Lock — Stand-Alone, No WiFi
Offline keypad cabinet lock for gym, office and parcel lockers. Battery-powered, 5-minute retrofit, audit-free simple deployment. PIN + MIFARE card, DC 6V, 4×AA.
This page already points to it as the next recommended reference.
Related blog posts
3
Fingerprint Drawer Lock: The Complete 2026 Guide to Biometric Drawer Security
Explore fingerprint drawer lock technology with detailed specs, types, installation guides, and use cases for home, office, and healthcare drawer security.
It supports the same product context: Office Cabinet Lock — PIN + Card for Filing & Pedestals, RFID Cabinet Lock — MIFARE Card, Offline Authentication, PIN Code Electronic Cabinet Lock — Stand-Alone, No WiFi.
Fingerprint Locker Lock: The Complete Guide to Biometric Locker Security in 2026
Learn how a fingerprint locker lock upgrades gym, school, and workplace locker security with biometric access control. Compare models, features, and installation options.
It supports the same product context: PIN Code Electronic Cabinet Lock — Stand-Alone, No WiFi.
EMS Cabinet Lock: DEA-Compliant Drug Security for Paramedic Vehicles
EMS cabinet lock guide covering DEA Schedule II compliance, dual-authentication, tamper-evidence, audit trail, vehicle power, and ePCR integration for ambulance fleets.
It supports the same product context: Office Cabinet Lock — PIN + Card for Filing & Pedestals.
Specify your hotel project with our engineers
Send your room count, ceiling type, and protocol preference. We will return a sample plan and quote within 24 business hours.
- Move from general guidance into a product or application discussion.
- Use RFQ when pricing, drawings, MOQ, or launch timing needs structure.
- Keep a direct contact path visible for fast clarifications and handoff.